Features Pricing Join Waitlist
AI-Powered DAST Scanner

Find Vulnerabilities
Before Attackers Do.

AI-powered OWASP Top 10 scanning that doesn't just find vulnerabilities, it proves they're exploitable with real attack chains. Deep security testing for modern web applications.

Launching soon. Be the first to know.
ReconBug mascot
How it works

Here's how we protect you

Add Target
Target URL
https://example.com
DNS Verification
TXT reconbug-verify=a8f3...
Verify & Add
Ownership verified
01

Register your domain

Type your URL, verify ownership, and you're in. Takes 30 seconds.

Crawler · example.com
67%
/
├─/login PAGE
├─/api/v1/users API
├─/dashboard PAGE
│ └─/settings FORM
├─/api/v1/auth API
└─/upload FORM
47 endpoints 12 APIs 8 forms
02

Crawl entire website

Discover every single endpoint: pages, APIs, forms, hidden routes. Nothing is missed.

$ reconbug scan --owasp
example.com 47 endpoints
✓A01: Broken Access ControlCLEAR
✗A03: SQL InjectionCRITICAL
✗A07: XSS ReflectedHIGH
✓A02: Crypto FailuresCLEAR
✗A05: Security MisconfigMEDIUM
A10: SSRFRUNNING
03

Scan every endpoint

170+ security checks based on the OWASP Top 10. SQL injection, XSS, broken auth, all covered.

✦ Where other scanners stop ✦
AI Agent · Deep Analysis
◆SQLi on /api/v1/users accepts UNION...
◆Session token lacks HttpOnly flag...
▸Testing auth bypass via token reuse
!IDOR: /api/v1/users/{id} returns other users
◆Combining SQLi + IDOR + session...
★Chain found: Full account takeover
◆Analyzing 3 more edge cases...
04

AI digs deeper

Our AI agent reasons like a real pentester, chaining findings, testing edge cases, finding what automated tools miss.

Exploit Chain #1
Account Takeover CRITICAL
SQLi on /api/users Medium
Session token leak Low
IDOR on /users/{id} Low
3 low/medium vulns = full account takeover
05

Prove it's exploitable

Small issues combine into real attacks. We chain vulnerabilities and show exactly how an attacker would use them.

Scan Report · example.com
D+
Security Score 7 issues found
Critical
2
High
1
Medium
3
Low
1
Download PDF Report
06

Get a clear action plan

Prioritized findings with step-by-step fix instructions. Download as PDF, share with your team.

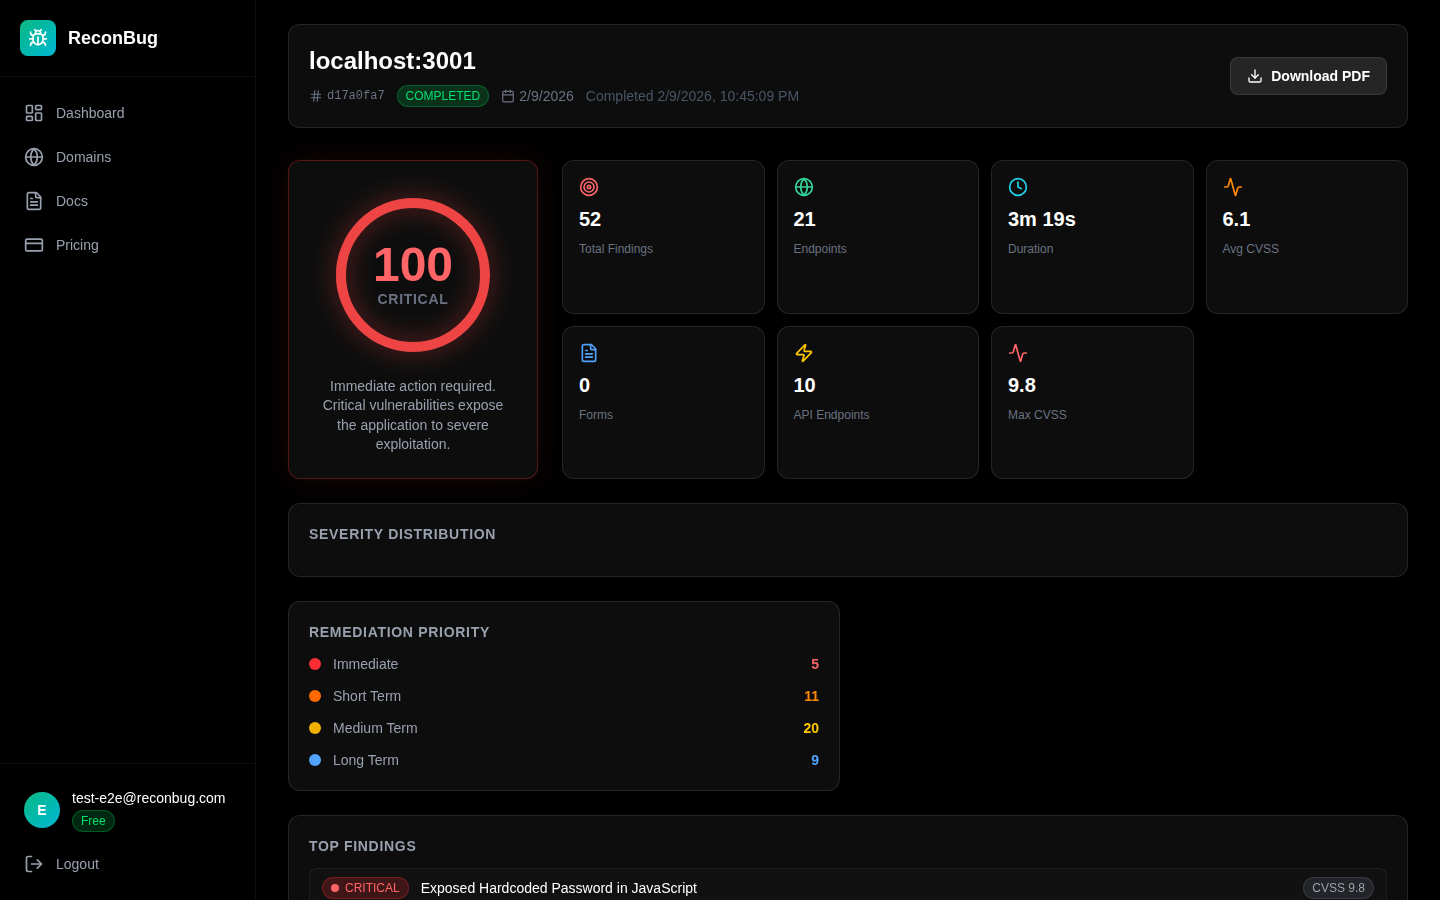
See What ReconBug Finds

Real scan results. Real vulnerabilities. Proven exploitable.

reconbug.com/dashboard
ReconBug scan results dashboard

20 Attack Modules. Zero Blind Spots.

Reconnaissance. Exploitation. Proof of concept. All automated.

reconbug --scan --modules
$ recon --passive [9 modules]
▸ WHOIS Lookup Domain registration, registrar, expiry
▸ DNS Enumeration A, AAAA, MX, TXT, NS, SOA records
▸ Subdomain Discovery CT logs, passive sources
▸ Technology Detection CMS, frameworks, libraries
▸ SSL/TLS Analysis Certificates, protocols, expiry
▸ Security Headers HTTP security headers audit
▸ Email Harvesting Public email addresses
▸ Web Fingerprinting WAF detection, robots.txt
▸ Shodan Intel Infrastructure intelligence
$ attack --owasp-top10 [11 modules]
▸ A01: Broken Access Access control vulnerabilities
▸ A02: Crypto Failures Cryptographic weaknesses
▸ A03: Injection SQL, NoSQL, OS, XSS injection
▸ A04: Insecure Design Design & architecture flaws
▸ A05: Misconfig Security misconfigurations
▸ A06: Vuln Components Outdated dependencies & CVEs
▸ A07: Auth Failures Identity & authentication
▸ A08: Data Integrity Software & data integrity
▸ A09: Logging Fails Monitoring & alerting failures
▸ A10: SSRF Server-side request forgery
▸ Exceptions Error handling & exception leaks
$ Ready. Awaiting target.
Simple, Transparent Pricing

Enterprise Security,
Startup Pricing

One plan. Scale as you grow. Cancel anytime.

Save 66%
Starter
€17
/month
Billed at €199/year
5
Assets
15
Scans/mo
  • Full OWASP Top 10
  • All vulnerability checks
  • PDF reports
  • Exploit chains
Join Waitlist
Business
€50
/month
Billed at €597/year
15
Assets
45
Scans/mo
  • Everything in Pro
  • 15 domains / subdomains
  • 45 scans per month
  • Priority support
Join Waitlist

Need more? Scale up to 50 assets & 150 scans/mo in the dashboard.

Frequently Asked Questions

One simple plan starting at €17/month (billed annually at €199/year) or €49/month. It includes 5 assets and 15 scans/month. Need more? Scale up with our multiplier. Each step adds 5 assets and 15 scans. Up to 50 assets.

Yes. You must verify domain ownership via DNS TXT record and sign a scan authorization agreement before active scanning begins. This ensures legal compliance.

ReconBug doesn't just report possible vulnerabilities, it proves they're exploitable. Our AI-powered scanner validates each finding with real exploit attempts, dramatically reducing false positives.

All OWASP Top 10 categories: SQL injection, XSS (reflected, stored, DOM), SSRF, CSRF, IDOR, deserialization, race conditions, exploit chains, and much more.

Yes, cancel anytime from the billing portal. You keep access until the end of your current billing period. No questions asked.

Ready to Secure Your Web Applications?

AI-powered vulnerability scanning that proves exploitability. Launching soon.

Join the Waitlist